It's a common whisper in our field: "Security is solely a backend concern." 🛡️
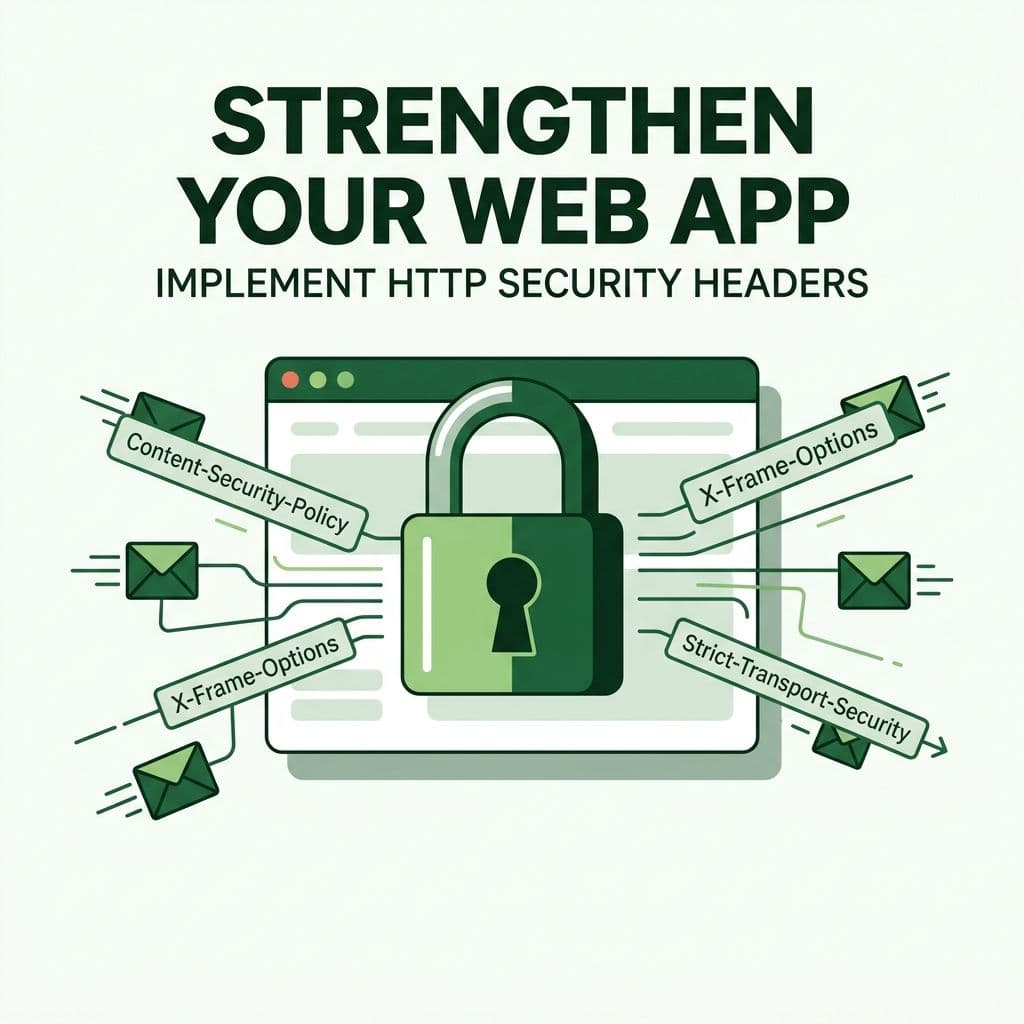
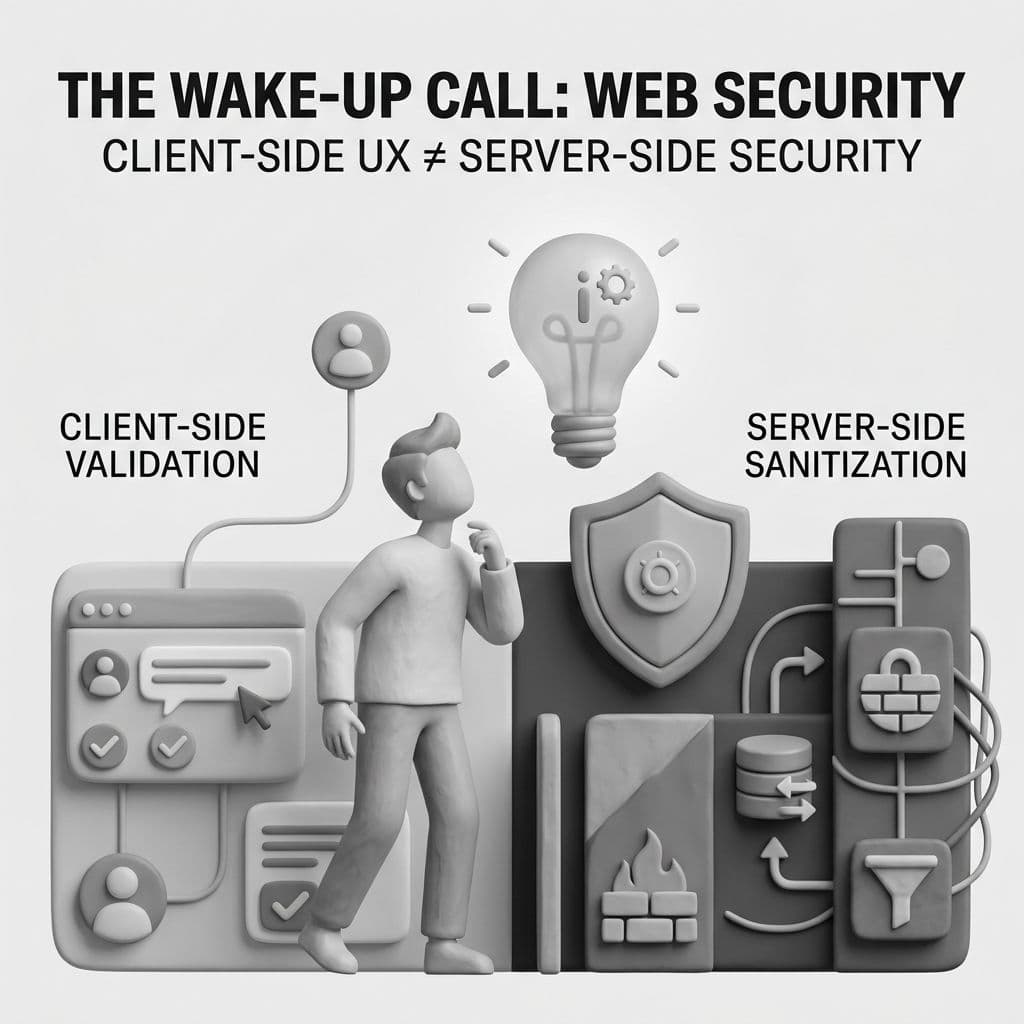
I've seen firsthand how dangerous this assumption can be. Thinking that client-side code is just for display, and not a potential attack vector, is a recipe for disaster. From insecure direct object references to improper API key handling, the frontend holds critical pieces of the security puzzle.
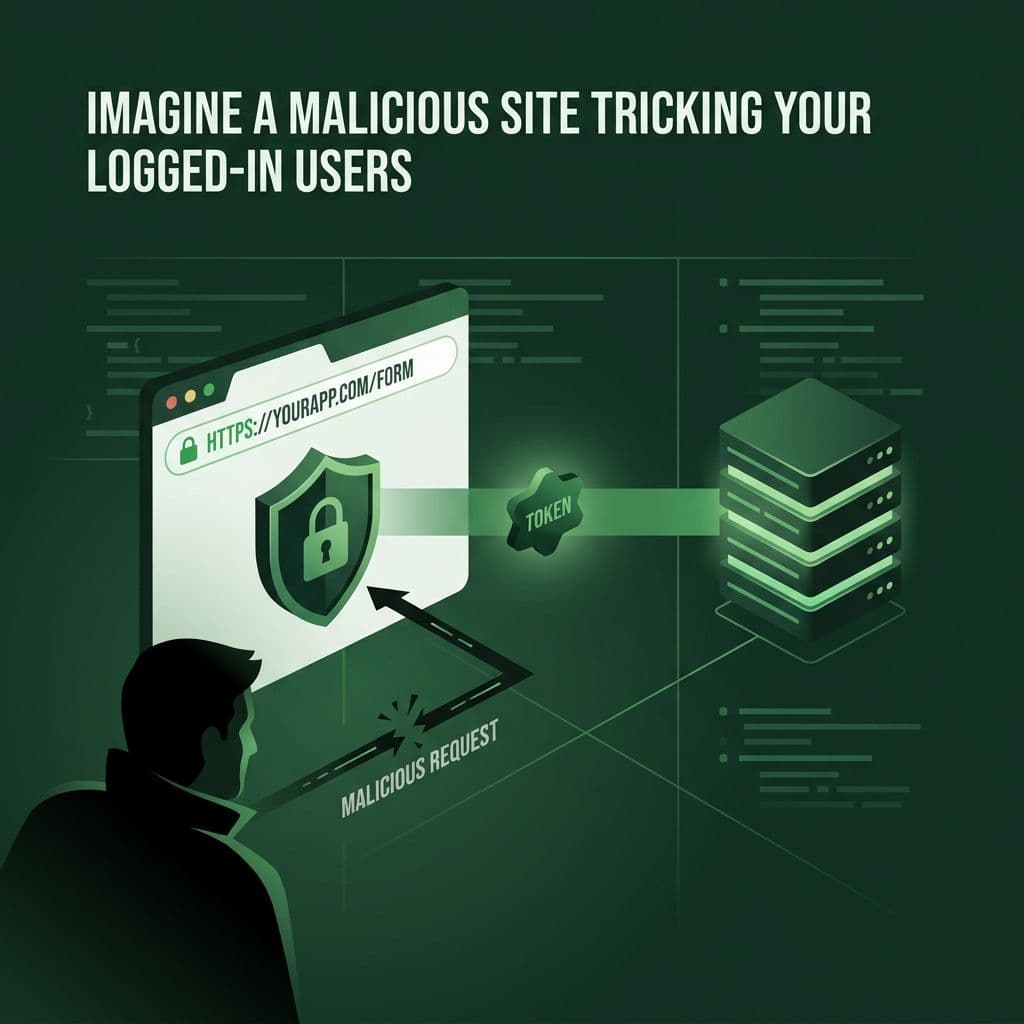
A simple form, for instance, might rely on client-side validation for input. While helpful for UX, if the backend doesn't re-validate, a malicious user can easily bypass it, sending bad data straight to your database. It's a stark reminder that every layer matters.
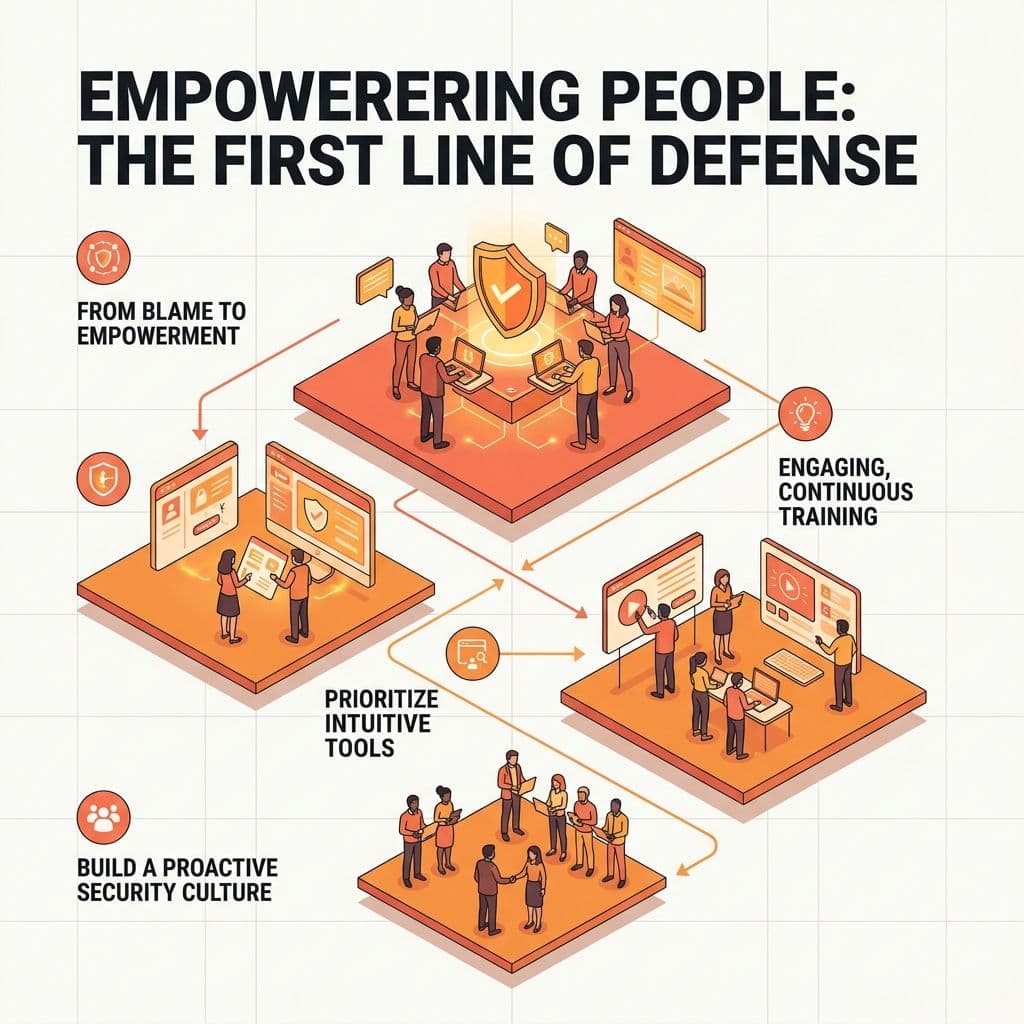
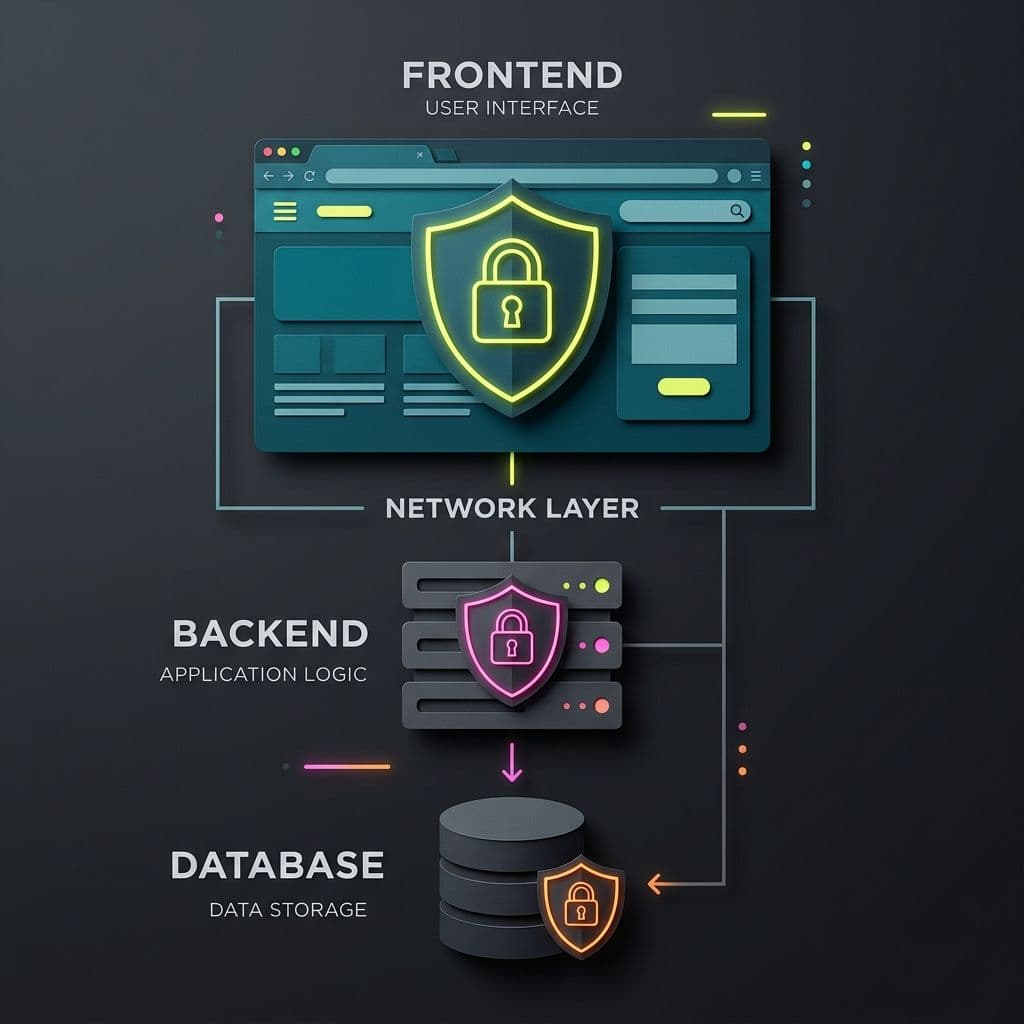
Building secure applications means a holistic approach. Frontend code isn't just pretty pixels; it's a crucial gatekeeper and a point of interaction with sensitive data. Investing in secure coding practices across the entire stack, right from the browser, is non-negotiable.
#FrontendSecurity #WebSecurity #FullStackDevelopment #Cybersecurity #DevOps #MERNStack #NextJS
…more